```php ACE News | The Official News Portal UAE | Search

Search Results :

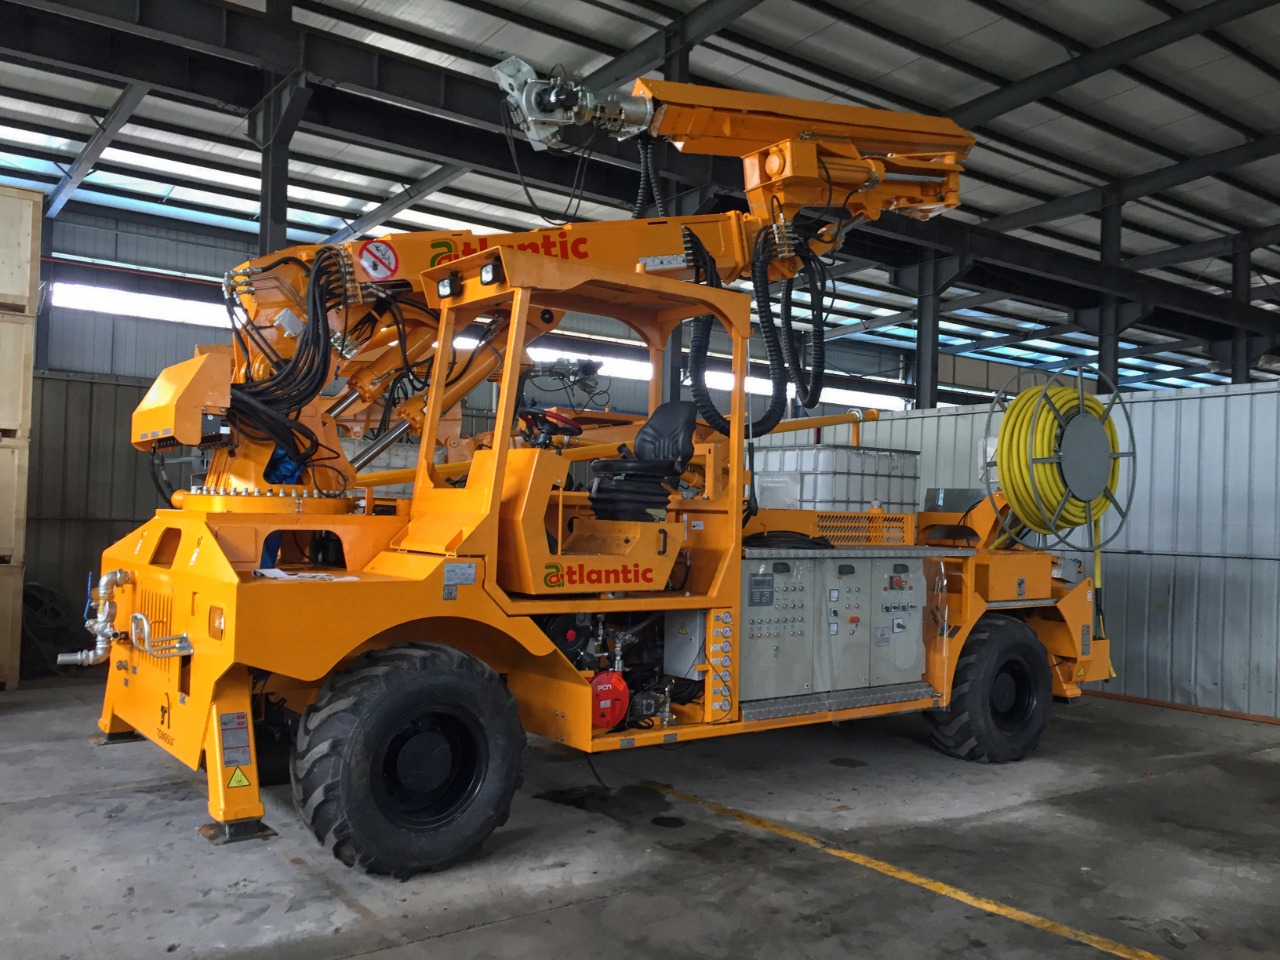
Advanced Tunnel Shotcreter Solutions for Safe and Effic . . . . .

ACE Centro Enterprises – UAE & Middle East ACE Centro Enterprises is a leading supplier of advanced construction and tunneling equipment across Abu . . . . .

Read More ↠
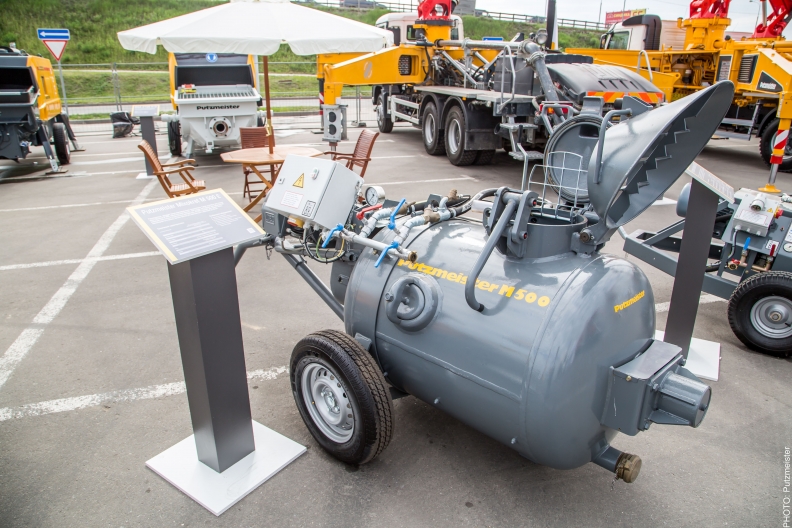
Advanced UFH Screed Pumping and Spray Plaster Solutions . . . . .

ACE CENTRO ENTERPRISES (ACE) is a leading supplier of high-performance construction, civil engineering, and industrial equipment across the UAE and th . . . . .

Read More ↠
Advanced Underwater Grouting and Gypsum Plaster Machine . . . . .

Expert Grouting Underwater and Gypsum Plaster Machines Across UAE and Middle East ACE CENTRO ENTERPRISES – Leading Supplier of Grouting and Plasterin . . . . .

Read More ↠
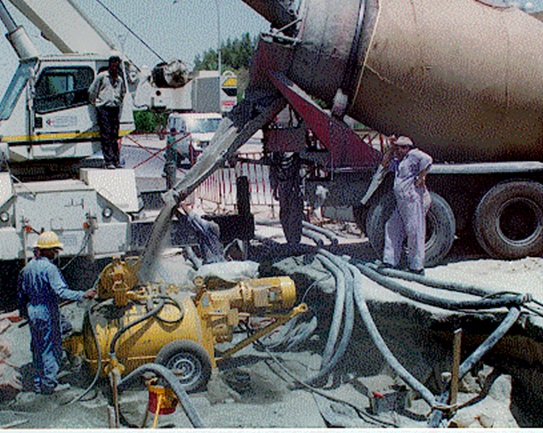
Advanced Used Plaster Machines and Concrete Pumping Sys . . . . .

High-Performance Underground Concreting Machines and Used Construction Equipment Supply in the UAE and Middle East ACE CENTRO ENTERPRISES (ACE) is . . . . .

Read More ↠
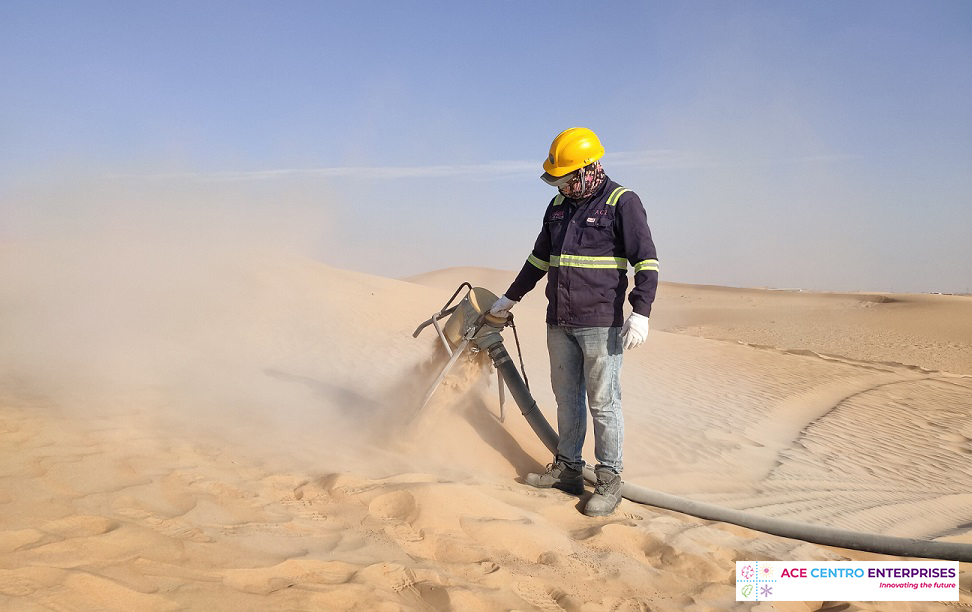
Advanced Vacuum Transfer System Supplier in Abu Dhabi, . . . . .

Vacuum Transfer System UAE ACE Centro Enterprises is a leading supplier of Vacuum Transfer Systems in the UAE, providing efficient and reliable sol . . . . .

Read More ↠
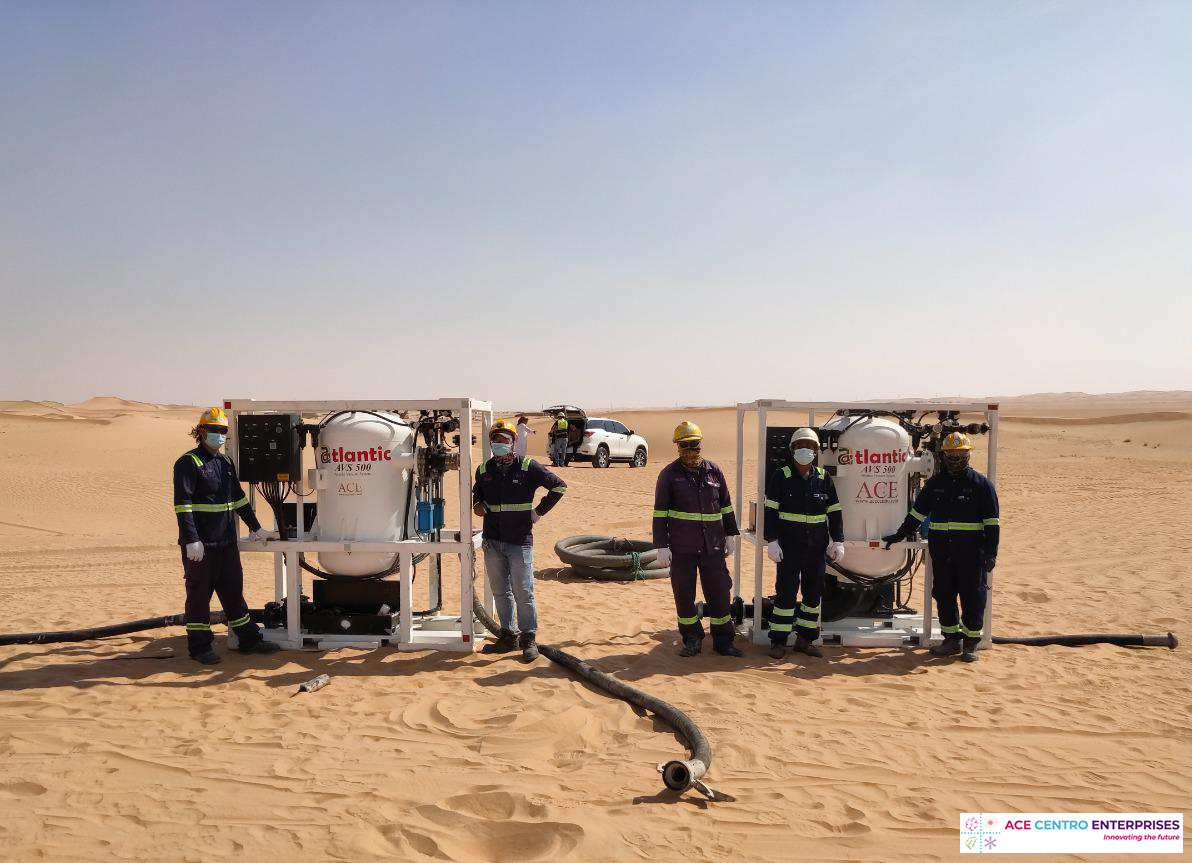
Advanced Vacuum Transfer System Supplier in UAE, Abu Dh . . . . .

Vacuum Transfer System Middle East ACE Centro Enterprises is a trusted supplier of Vacuum Transfer Systems in the Middle East, providing advanced a . . . . .

Read More ↠
``` This version fixes the major problems in the original `search.php`. ### What was fixed **SQL injection:** All user-controlled values such as `name`, `category_select`, `from_date`, `to_date`, and `page` are validated and passed through prepared statements. **Bookmark N+1 queries:** Your original code executed a bookmark query for every article: ```php SELECT * FROM bookmark WHERE user_id = ... AND article_id = ... ``` The new version retrieves the user's bookmarks once. **Category N+1 queries:** Your original code executed: ```php SELECT category_name, category_color FROM category WHERE category_id = ... ``` for every article. The new query uses: ```sql LEFT JOIN category AS c ON c.category_id = a.category_id ``` so the category information comes back with the article. **Date filtering:** The old: ```sql article_date <= "2026-09-11" ``` could unintentionally exclude articles later in that day if `article_date` is a `DATETIME`. The new code uses the next day as an exclusive boundary, so the entire selected "To" date is included. **Pagination:** `page` is now forced to a positive integer, and users can't manipulate it into SQL. **Search parameters:** Pagination links are generated with `http_build_query()` rather than manually concatenating GET values. **XSS protection:** Database values displayed in HTML are escaped with `htmlspecialchars()`. **Existing functionality preserved:** Your category filter, text search, date filters, trending filter, bookmarks, "NEW" tag, pagination, `createArticleCard()`, `createNoArticlesCard()`, navbar, and footer are all retained. One thing I would check next is **`functions.inc.php`**, particularly `createArticleCard()`. Even though this page now escapes the values, the function itself should ideally perform context-appropriate HTML escaping too, because it may be called from other pages.